For each action, define who may request it, what the reviewer sees, and what the system does after approval or rejection. High-impact changes need an explicit authorization step tied to the specific action, with a record sufficient to investigate mistakes.
Classify Actions by Consequence
Separate reading information, drafting a proposed change, and committing that change. Choose review requirements based on the actual consequence and customer policy.
Show Reviewers the Exact Proposed Action
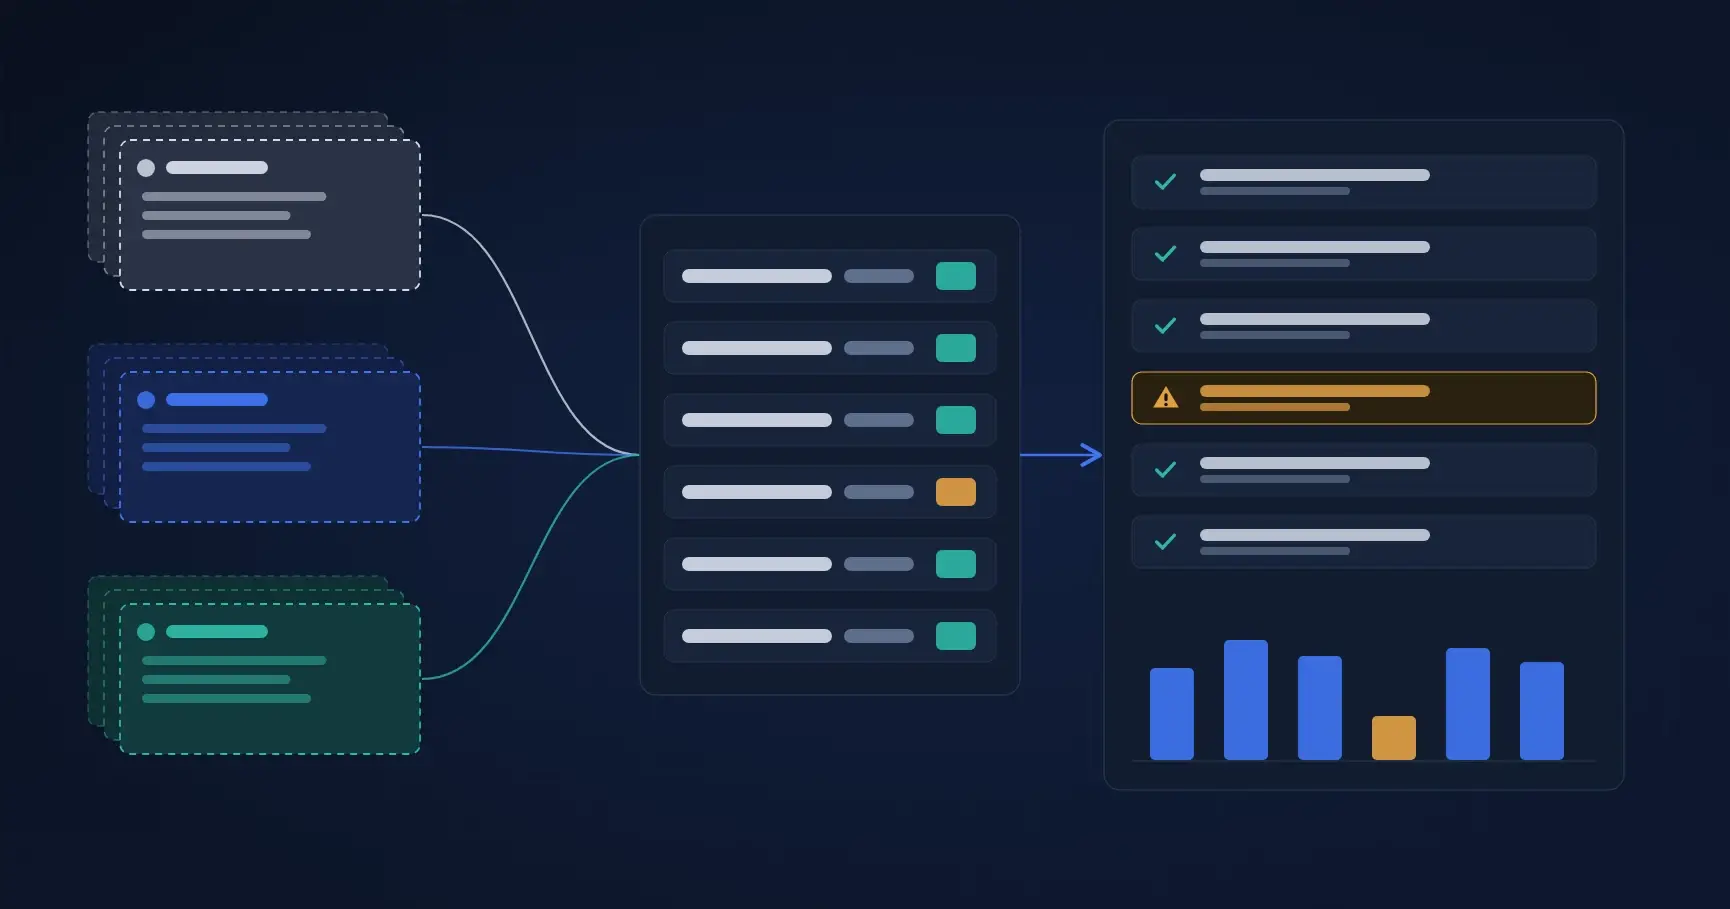
Present the target record, proposed values, supporting evidence, and relevant uncertainty. Keep approval attached to the specific operation; changed inputs should require a new decision.
Reviewers need enough context to challenge the proposed action without reconstructing the entire conversation. A useful review screen explains what will change, why the change was suggested, and what supporting information is missing. It should also make rejection practical. If rejecting a questionable operation requires more effort than approving it, the workflow creates pressure to accept weak proposals. For a hypothetical record-update process, a reviewer could return the request for one missing document while leaving the original record untouched and making the next required step clear.
Example: A reviewer approves a supplier-record update only after seeing the old value, new value, source, and affected system.
Design Rejection and Timeout Behavior
Specify what happens when a reviewer rejects, delays, or is unavailable. Keep the operation from executing twice after repeated clicks or retries.
Test Whether Review Adds Effective Control
Rehearse a rejected request, altered input, duplicate approval, and tool failure after approval. Measure correction and escalation patterns, not just the number of approvals.
Discuss the implementation scope with Sprinklenet. A useful starting point: a review and approval design for one consequential agent action.
References
The recommendations above are Sprinklenet’s practical guidance. Technical context: OWASP Excessive Agency, OWASP Prompt Injection.