For each connector, document the authenticated identity, permitted records, allowed actions, credential owner, and revocation process. Test access changes and failures. A connector that retrieves the right file with excessive permissions is still a weak integration.
Identify Whose Authority the Connector Uses
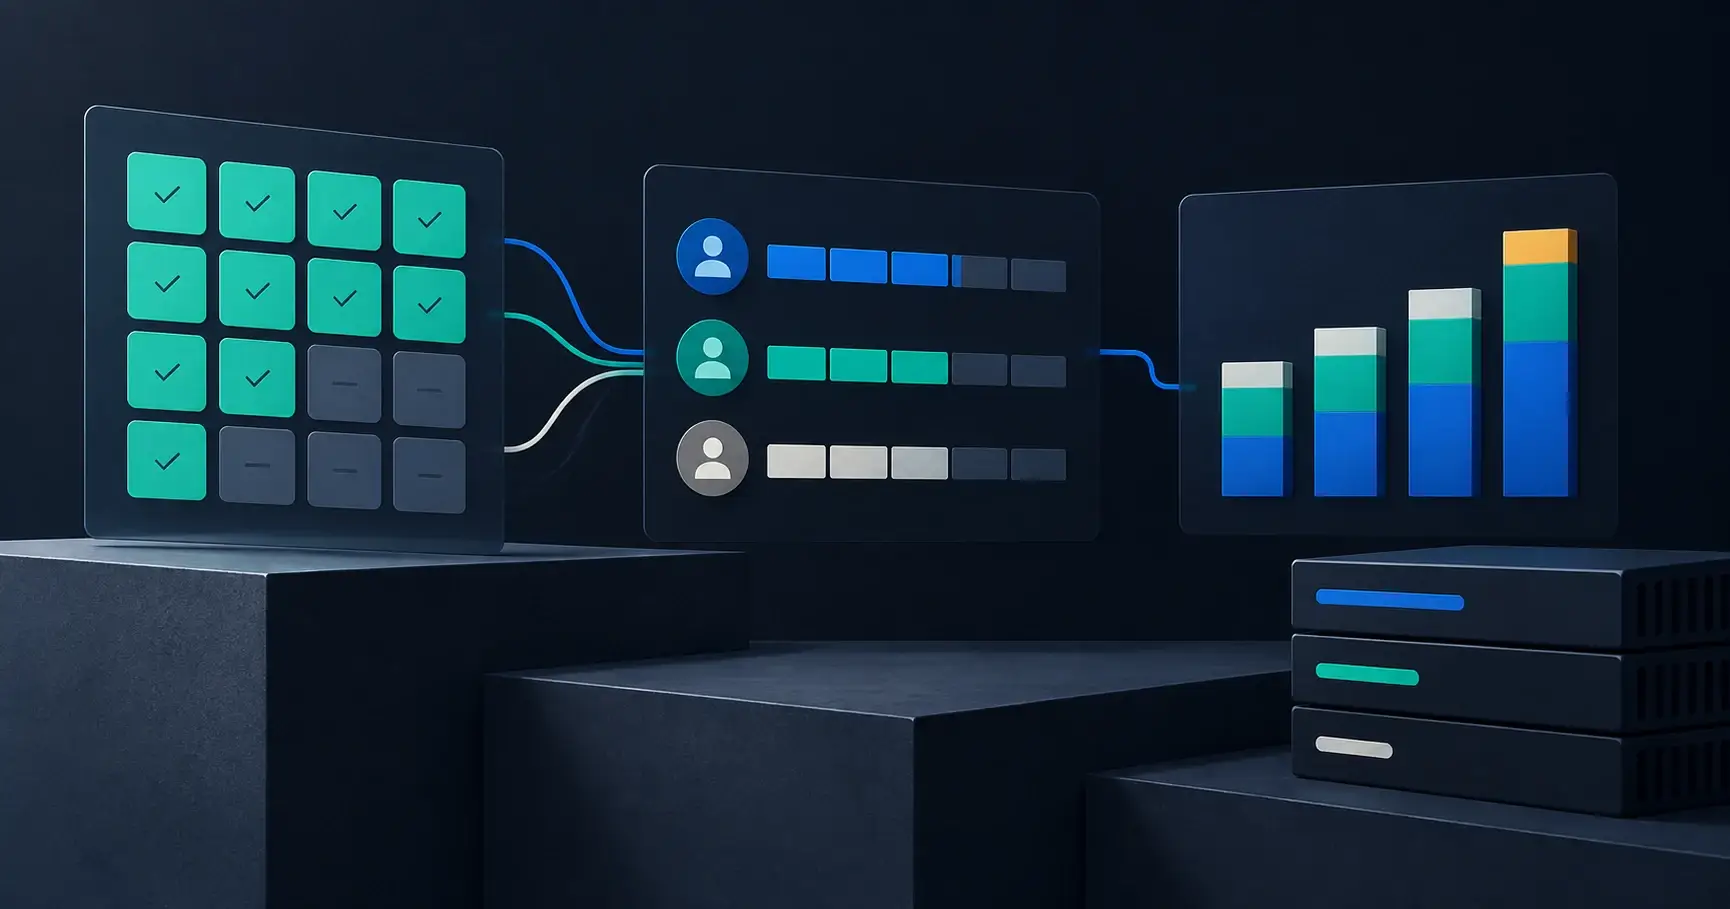
Record the signed-in user or service identity, accessible records, credential owner, and allowed actions. Explain the tradeoff between delegated user access and broader service access for the specific task.
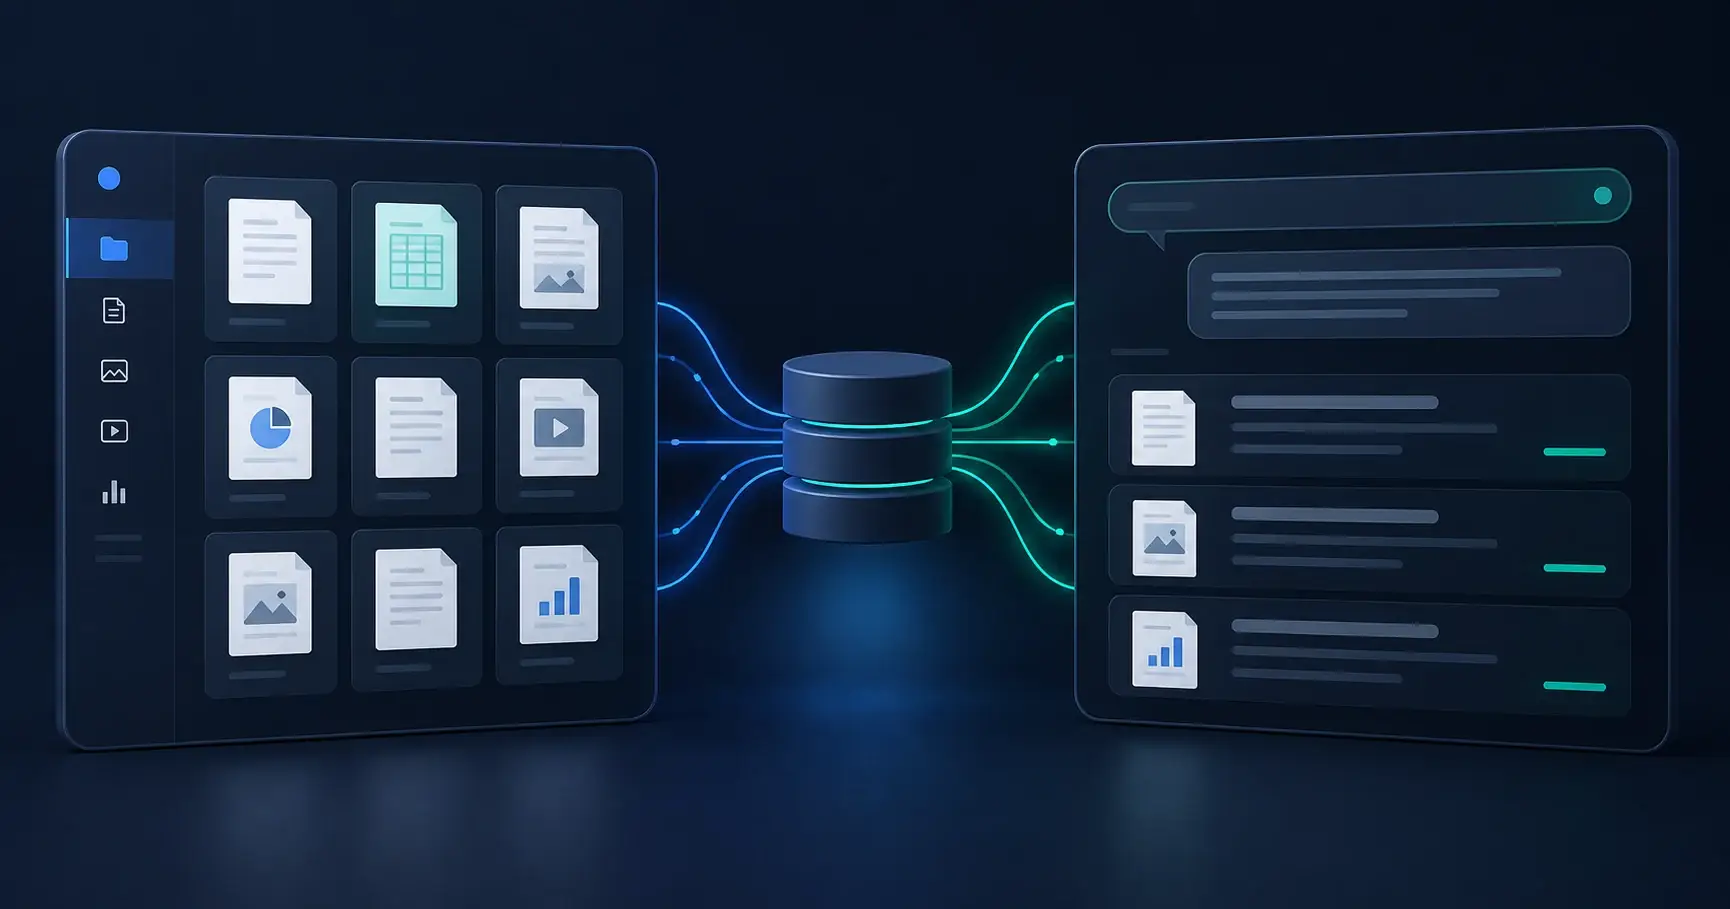
A background import may use a service identity because no employee is signed in when it runs. That identity can see a collection broader than any individual user should receive. The application therefore needs a separate, tested decision about which imported passages may be returned to each requester. In a hypothetical design review, ask the team to trace one restricted document through import, storage, retrieval, and display. This exposes whether access is preserved throughout the process or merely assumed because the original repository has permissions.
Separate Reading From Changing Records
Use distinct scopes or tools for retrieval and consequential writes where supported. Limit each operation to the records and parameters it needs.
Example: A document-search connector should not inherit the power to delete files merely because the provider offers that permission.
Test Revocation and Failure
Remove a user permission or credential and confirm the observed behavior. Test expired credentials, rate limits, retries, and interrupted synchronization without allowing silent stale-data assumptions.
Document the Operating Contract
Specify refresh expectations, access changes, audit evidence, recovery owner, and credential rotation ownership. Include connector maintenance and upstream API changes in the support scope.
Discuss the implementation scope with Sprinklenet. A useful starting point: a connector permission and failure-mode review for one source system.
References
The recommendations above are Sprinklenet’s practical guidance. Technical context: OWASP Excessive Agency, Microsoft SharePoint Agent Access.